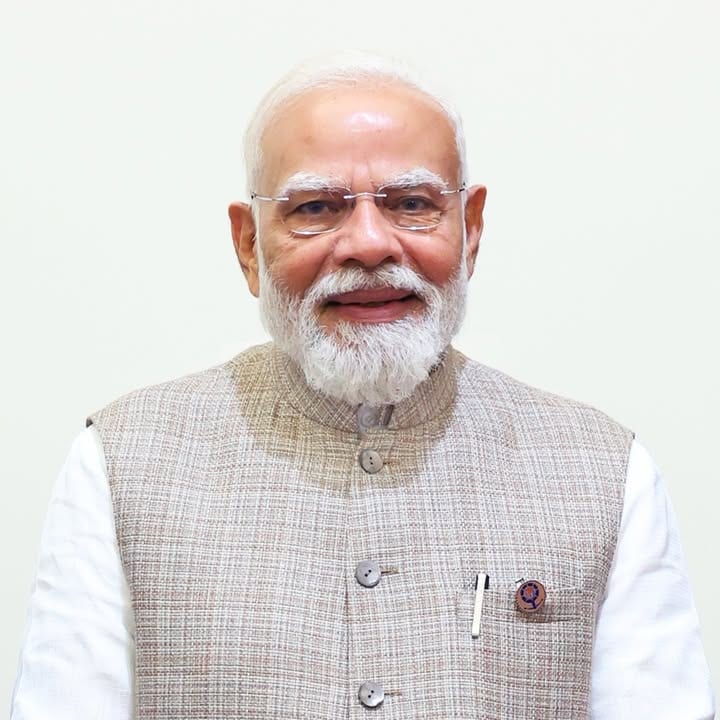
Prime Minister Narendra Modi inaugurated the Reserve Bank of India's Rs 169-crore data centre and Cybersecurity Training Institute in Bhubaneswar on October 25, warning that modern wars are no longer confined to borders. "Wars being fought by attacking economies," he said, flagging "cyber terrorists" as a direct threat to India's financial stability, according to NDTV.
The facilities will benefit Odisha and the country, Modi said. The next decade will focus on making Indian banking more efficient and reliable after a ten-year expansion that took financial access to millions of new customers, LiveMint reported.
The Bhubaneswar campus moves a piece of the country's financial infrastructure eastward, away from the concentration that has long defined India's banking sector. For the central bank, the location signals that critical nodes must be dispersed if the digital economy is to remain resilient.
The Cyber Threat Is Now an Economy-Wide Weapon
Modi's language was direct. Wars are being fought by attacking economies, and cyber terrorists now operate with the same strategic intent as conventional adversaries. The financial system, UPI rails, online banking portals, market infrastructure, has become a high-value target. A successful breach need not empty a vault; it can freeze payments, lock out customers and corrode the trust that digital money depends on.
India spent the last decade wiring millions of people into formal banking. That expansion enlarged the attack surface. Every new account linked to a phone number, every merchant QR code, every API bridge between a fintech and a core banking system is a door that must be defended. Efficiency is no longer enough; reliability under attack is the new standard.
At the Bhubaneswar event, Modi also used the language of theft: the banking system must be protected from "cyber looters" and "cyber terrorists," as LiveMint reported. The two terms differ. A looter wants money; a terrorist wants disorder. The second is more dangerous for a payments economy, because it seeks to destroy confidence in the rails themselves.
A Sovereign Cyber Spine, Not a Vendor's Extension
The choice to build indigenous data storage and a training institute inside the RBI's institutional ecosystem is a statement of intent. It is cyber sovereignty made concrete. Rather than renting resilience from overseas vendors, the central bank is expanding its capacity to store financial data and to train personnel who will respond when an attack begins. The training institute is the less visible half of the inauguration; in a crisis, it may prove the more useful one.
Yet a single data centre cannot secure a system whose weakest points are often small cooperative banks and non-bank lenders. The structural fault-line is uneven cyber hygiene. A large commercial bank may run 24-hour security operations; a cooperative bank in a district town may rely on a single vendor and a backup tape. The Bhubaneswar institute will deliver its full value only if it becomes a mandatory drill floor for these smaller institutions, not a venue reserved for headline exercises.
The Rs 169-crore figure is small next to the balance sheets of India's largest banks. That is the point. Cyber defence does not require the biggest budget; it requires institutions to treat every access point as contested ground. A training institute can multiply its value for years, while a software purchase depreciates. The central bank has chosen a compound investment over a one-time fix.
Dispersal Lowers the Single-Point Risk
Locating critical financial infrastructure in Odisha reduces concentration risk. Mumbai and Delhi have carried India's financial plumbing for decades; that density is a liability when electricity grids, fibre routes and personnel clusters can all be targeted at once. A campus in Bhubaneswar does not eliminate the risk, but it creates a second spine. If one corridor is degraded, the other continues to settle payments and store records. That redundancy is a precondition for a digital economy that intends to keep functioning through a cyber conflict.
The Reserve Bank of India has long treated cyber risk as a supervisory issue. The Bhubaneswar facility shifts that posture from supervision to capability-building. The distinction matters: supervisors inspect compliance and penalise failures; capabilities absorb the attack and keep the system moving. A regulator that builds a training institute is signalling that it expects banks to practise defence, not promise it on paper.
The preference for indigenous storage carries a regulatory logic. Financial data generated by Indian users deserves an Indian home, not because foreign vendors are inherently unsafe, but because a sovereign economy must be able to guarantee continuity without asking permission from a jurisdiction it does not control. That continuity is the foundation of everything from retail payments to cross-border trade finance.
Regulators will need to match the physical investment with enforcement. A data centre alone does not clean up a cooperative bank that has not patched its core banking software in three years. The institute should issue threat intelligence and set drill schedules; the supervisory arm should penalise institutions that skip them. Nothing in Indian banking regulation forbids such a link, but the link must be made explicit.
The inauguration signals a shift in the central bank's disaster-recovery map. It no longer points only westward. The data centre will store records; the training institute will rehearse people. The harder challenge is to make cyber discipline as routine as cash reconciliation in every branch and payment app backend. The wall being built is not around India's economy; it is underneath it. How well the smaller banks and non-bank lenders climb onto that foundation will decide whether the Prime Minister's warning remains a speech or becomes operational reality.